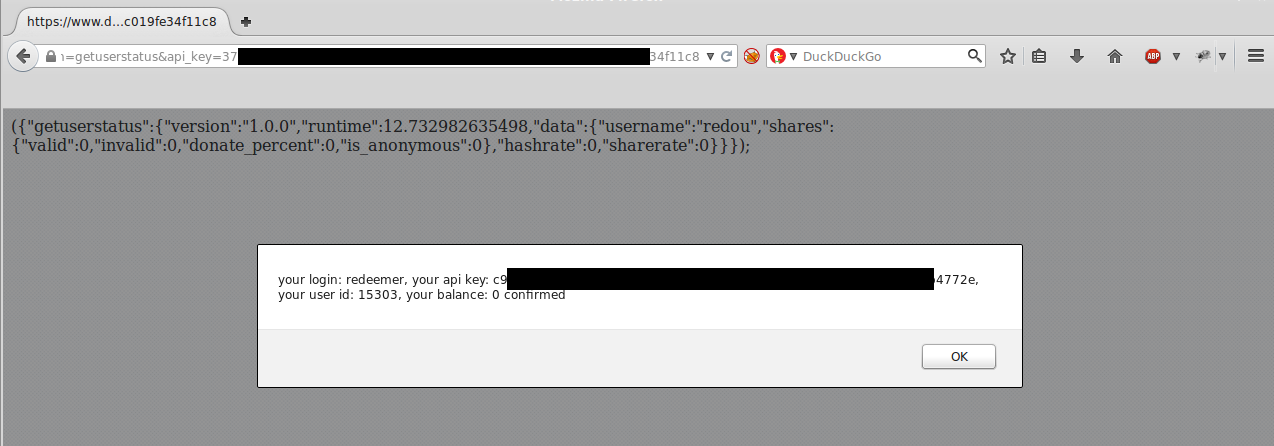
Vulnerable is callback parameter introduced in this commit. (note: Content-Type response header is text/html)
Attacker needs a valid api key. Usually he can get it by just signing up to a pool.
Example:
https://pool/index.php?callback=XSS&page=api&action=getuserstatus&api_key=VALID_API_KEY
Found and reported: 25.05.2014
Fixed: 10.06.2014
Ps. It was introduced after more or less security-related discussion here.
